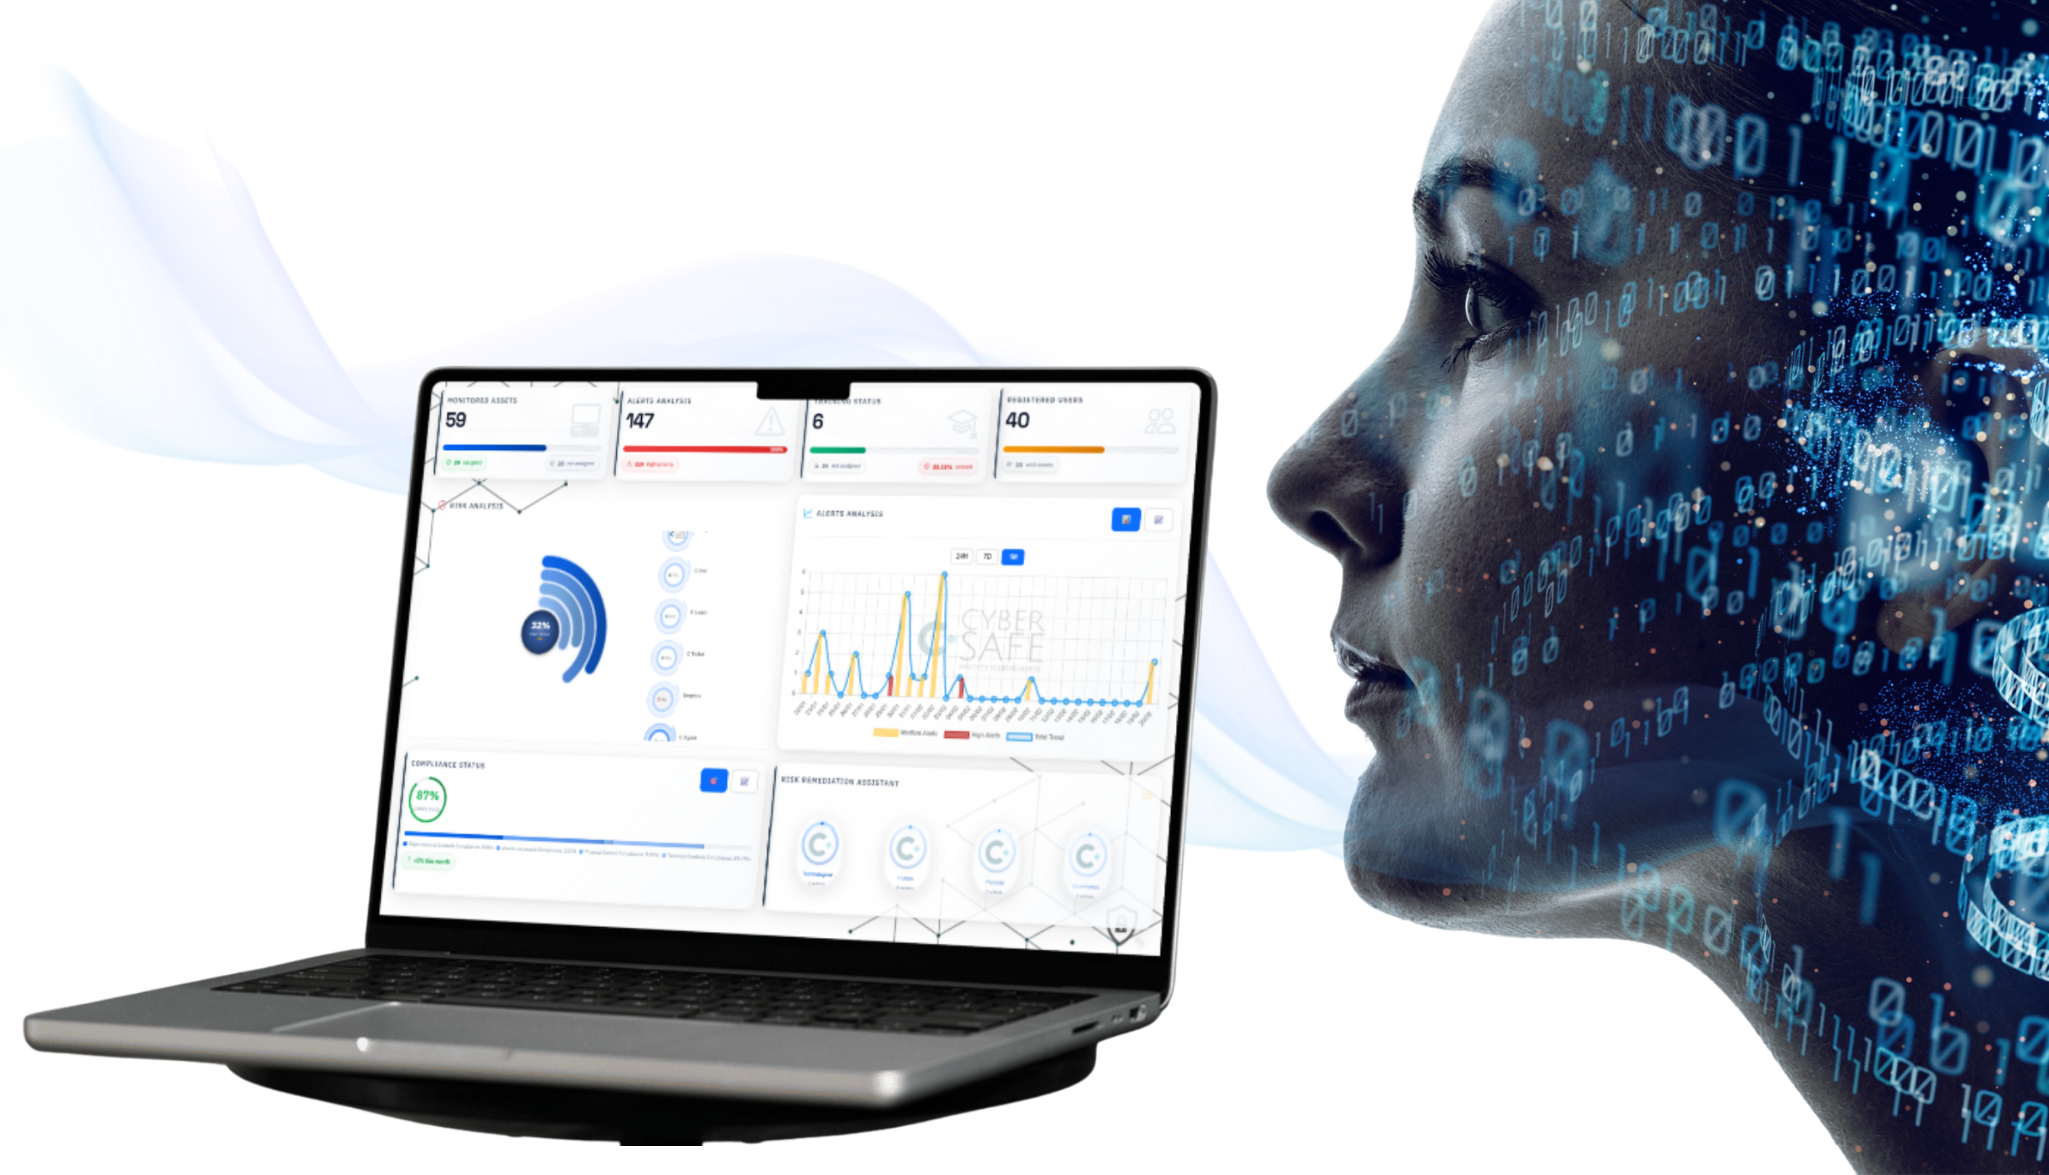
C-CyberSafe platform preview
Want to see the flow in a real case?

How it works

Once the reference framework (e.g., ISO 27001) is chosen, compliance is built by configuring the connectors that collect evidence. The configuration defines the baseline: minimum risk and potential compliance. Continuous monitoring then verifies over time how real risk and real compliance evolve.

C-CyberSafe platform preview

Step-by-step Schema

Activities follow a logical sequence over time: first the baseline is defined (setup), then the platform enters continuous monitoring and operational management (cycle).

1. Reference Framework

Define the framework or regulation to be respected (ISO 27001, NIS2, DORA, etc.).

Initial Setup

2. Connectors Configuration

Activate connectors that collect evidence on processes, systems, and people.

Initial Setup

3. Initial Baseline

From the configured coverage, obtain the baseline: minimum risk and potential compliance.

Initial Setup

4. Continuous Monitoring

Evidence collected over time measures drifts, alerts, and operational variations.

continuous cycle

5. Remediation and Control

Criticalities generate tracked actions: tickets, owners, deadlines, and history always available.

continuous cycle
1

1. Reference Framework

Define the framework or regulation to be respected (ISO 27001, NIS2, DORA, etc.).

2

2. Connectors Configuration

Activate connectors that collect evidence on processes, systems, and people.

3

3. Initial Baseline

From the configured coverage, obtain the baseline: minimum risk and potential compliance.

Initial Setup
4

4. Continuous Monitoring

Evidence collected over time measures drifts, alerts, and operational variations.

continuous cycle
5

5. Remediation and Control

Criticalities generate tracked actions: tickets, owners, deadlines, and history always available.

continuous cycle

The CCyberSafe Model

We distinguish between what is structural (baseline) and what changes over time (monitoring). Compliance and risk are two views of the same phenomenon: control level and exposure.

Baseline

The configuration (coverage of controls and evidence) defines how "under control" you can be: minimum risk and potential compliance.

Monitoring

Over time, drifts emerge: technical drifts, operational exceptions, delays, non-conformities. The platform measures how real risk and real compliance change.

Governance

The company remains central: first we understand what is happening, then we decide whether to intervene or delegate, and to whom. Everything remains tracked (owner, deadlines, evidence, history).

Methodological rule: increasing coverage raises potential compliance and lowers minimum risk. Intervening on drifts maintains real compliance and real risk under control over time.

Trend of risk and compliance over time

Risk measures exposure. Compliance measures the level of control. Both evolve over time: the baseline depends on the configuration, the real depends on the drifts.

Rischio nel tempo
Rischio minimo (baseline) Rischio reale (monitoraggio)
alta bassa tempo →
La configurazione definisce il rischio minimo. Il monitoraggio misura il rischio reale: aumenta quando emergono scostamenti e segnali, e si riduce con remediation e controllo continuo.
Compliance nel tempo
Compliance potenziale (baseline) Compliance reale (monitoraggio)
molti pochi tempo →
La configurazione definisce la compliance potenziale. La compliance reale può ridursi nel tempo se mancano evidenze, aumentano eccezioni o si accumulano ritardi. Le azioni tracciate servono a mantenerla stabile.

From declarations to evidence

Connectors are not just integrations: they are the measurement layer that makes governance objective. Where possible, the platform collects automatic evidence; where necessary, it organizes input and responsibility.

Asset & endpoint

Patches, encryption, AV/EDR status, basic posture, inventory.

Backup & recovery

Executions, outcomes, alerts, coverage and recovery indicators.

Identity & access

MFA, privileges, access policies, anomalies and critical changes.

Awareness

Training, completion, deadlines, effectiveness measures.

Processes & remediation

Tickets, owners, SLAs, backlog, outcomes and history of actions.

Third parties & evidence

VRM, procurement, audit pack, evidence and segregation per customer.

Want to see the flow in a real case?

We activate your model of continuous monitoring of risk and compliance.

Request a demo